Four Advisory Disciplines. One Standard of Depth.
The team TinBOX brings to an engagement is the same team that led — not merely advised on — the programs they now advise others through. TinBOX LLC is a woman-owned, founder-led technology advisory firm based in Virginia.
Together they deliver TinBOX's fractional CISO, CPO, CTO, and CIO retainer — what other firms market as a vCISO or virtual CIO bench, staffed here by three named people instead of a rotating queue.
The Four Situations That Bring People Here
Most engagements start from one of these. If you recognize yours, the assessment is the fastest way to find out what it would actually take to resolve it.
Vendor Security Requirements
A strategic partner or enterprise customer sends a security questionnaire, and you realize you don't have the program to answer it honestly. Microsoft's third-party requirements. SOC 2 attestations. Vendor risk assessments that are gating the contract.
CMMC & Government Contracting
A government contractor needs CMMC compliance to keep or win a contract. The requirement doesn't scale with the size of your business. The consequences of non-compliance do.
AI Strategy
The pressure to adopt is real, and it's coming from the board, from competitors, and from employees already using it without a policy in place. Getting it right means addressing the data foundation, the workforce transition, and the governance layer at the same time, not in sequence.
Cloud & Technology Cost Crisis
Six months into the year and the IT budget is gone, consumed by cloud services that compounded quietly, vendors that were never rationalized, and software licenses nobody audited. The problem isn't IT. It's the absence of accountable technology leadership.
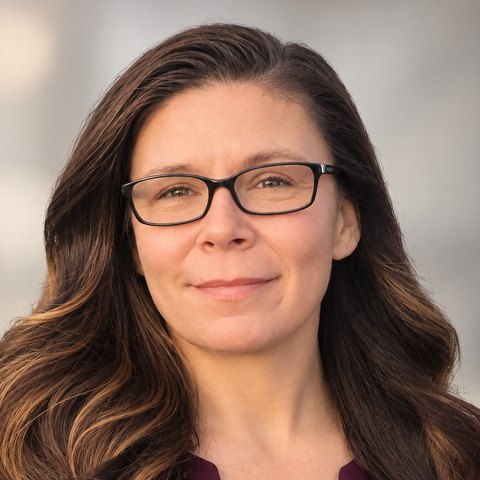
Jessica Dillon
Takes a technology estate that was designed for a smaller version of the organization and rebuilds it into one the business can scale on — while cutting what it costs to run.
spend reduction
MSP transitions
all international buildouts
Full background
The organizations that come to Jessica usually sense something before they can name it. The cloud spend that has quietly outpaced revenue. The managed services provider that has been billing for years without anyone with real technical authority asking what they're actually delivering. The compliance posture that passed its first audit and was never updated for the business that came after it. What looks like a collection of separate problems is almost always one: a technology environment designed for a version of the organization that no longer exists.
Her practice is built around that moment — the point where IT stops being overhead and becomes load-bearing infrastructure. She approaches compliance and cost reduction as the same problem: the vendor relationships creating exposure are usually the same ones creating the overhead, and resolving them as a single engagement is more durable than the sequential approach most organizations default to. For businesses in rapid growth, she builds and scales IT ahead of the curve, across multiple locations and international offices. At that pace, IT doesn't support the business from behind; it has to stay far enough ahead that the business never catches up to it.
The part clients tend not to anticipate is the commercial side. Most technology problems at scale are vendor problems in disguise: the MSP that made sense at one stage and hasn't been renegotiated since, the software portfolio that grew by accretion, the contracts nobody with technical authority has read. Jessica has negotiated, restructured, transitioned, and offboarded MSP relationships while protecting continuity and organizational knowledge — and she knows when to keep something outsourced, when to bring it in-house, and when a hybrid model is the only arrangement that actually holds.
The hardest part of AI adoption isn't the technology; it's the human problem. Jessica built an AI adoption strategy from the ground up — training programs, weekly discussions, regular knowledge exchange that kept an entire organization current without overwhelming it — while helping leadership navigate the uncertainty AI introduces at every level of the workforce. The organizations that get this right build the literacy first and let capability develop, rather than making reactive decisions about their people.
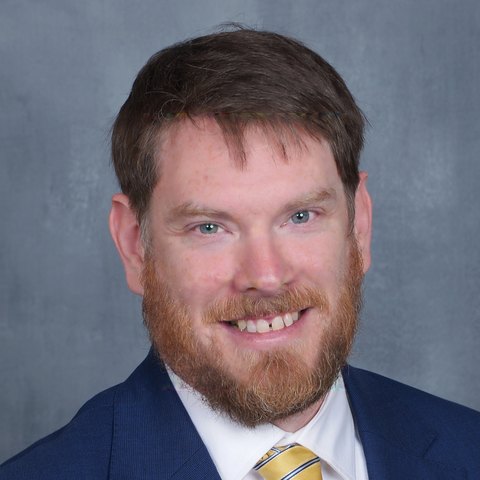
Eric Felix
Builds the security and privacy program that answers the questionnaire gating your contract — with privacy coverage across ten countries built in, not stapled on.
enforcement actions
secured
cleared annually
Full background
Most organizations don't think seriously about their security posture until someone else requires them to. A vendor security questionnaire from an enterprise partner. A CMMC requirement attached to a government contract. A cyber insurance renewal that starts asking questions nobody can answer confidently. A market expansion that brings three new privacy jurisdictions into scope. The trigger is external, the exposure is internal, and the gap between what the program looks like on paper and what it would look like under scrutiny is usually wider than anyone wants to find out.
Eric has spent his career on the inside of that gap. The government side of his background gave him something most practitioners don't get: volume. When you've built compliance programs at that scale, the requirements stop feeling like checklists and start becoming instinct — you stop reading what a control says and start seeing what it's actually protecting. Organizations rarely face one compliance obligation at a time; they face several, with overlapping controls, competing timelines, and auditors who aren't waiting on the other work in progress. Eric treats those overlapping requirements as a single design problem rather than a queue of certifications to work through.
A separate part of his practice, and one that hits closer to home for many clients, is vendor security assessments. Enterprise partners impose their own third-party risk programs on their suppliers, and the requirements are detailed and not forgiving of organizations without the right program in place. Increasingly those requirements extend into how organizations adopt AI — acceptable use, data handling, third-party model risk — and Eric has designed those frameworks from the inside rather than retrofitting them after the fact. When an incident occurs, he leads the orchestration rather than the technical remediation: coordinating legal, communications, response teams, and regulatory notification simultaneously, in the right order, under pressure.
What sets his practice apart is that the security and privacy sides carry genuine equal weight. His privacy work spans regulatory compliance across ten countries and extends into the architecture of AI-powered applications, where privacy by design and security by design are the conditions under which those systems can be built responsibly — not optional considerations.
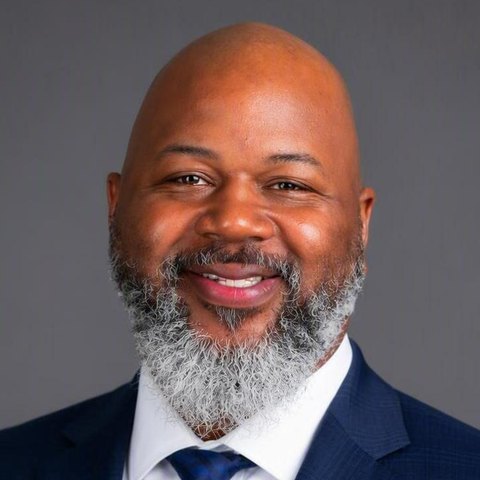
Sean Tucker
Finds the architectural decision that quietly became load-bearing, and resolves it before the cost of reversing it outgrows what the business can absorb.
reduction
reduction
sustained
Full background
Sean has a particular view of technical debt: the interesting version isn't the code that needs refactoring. It's the architectural decision that looked reasonable at the time and became load-bearing in ways nobody anticipated. The SaaS platform chosen for speed of implementation, now deeply embedded in workflows never designed around it. The cloud environment that expanded to meet a deadline and was never rationalized back into the broader picture. The AI-assisted prototype that shipped fast and then couldn't be extended by anyone who didn't write it. These decisions don't announce themselves as expensive mistakes — they compound quietly, in infrastructure costs, in delivery friction, in the data you can't trust and the systems you can't change.
The chasm between a business decision and its technology consequence is where most organizations lose years. Sean operates in that gap, translating what leadership is trying to build into architecture that can actually hold it, and surfacing the technical constraints that should be shaping strategy before they become the reason you missed a window. He rebuilt one organization's on-network posture and delivery pipeline as a single design problem — a zero-trust model where cloud, on-premises, and hosted infrastructure operated as one logical boundary rather than three environments to manage — cutting engineering rework by 25% while sustaining 100% audit readiness across ISO and FedRAMP.
His AI strategy work is forensic as much as forward-looking, helping organizations that have moved fast with AI-assisted development understand what they've actually built, where the structural risks sit, and how to extend it without compounding what's already there. For growing businesses that can't yet justify a full-time CTO, or that need an independent voice their internal technical leaders don't have, Sean is the judgment that prevents the bet that sets you back two years.
The other side of his practice is the build. Organizations designing new platforms, standing up data infrastructure, or making foundational technology decisions for the first time face a different version of the same problem: the choices that feel like implementation details are actually architecture, and architecture is hard to change once the business has grown around it. Sean works with those organizations before the decisions compound — shaping how data moves, where it lives, how it gets used, and whether the system being built can answer the questions leadership will be asking in two years.
Founded in 2018, TinBOX LLC is a woman-owned technology advisory firm based in Virginia. No rotating bench of unnamed contractors between you and the people whose names are on this page.
Want to talk to the team directly?
No rotating bench of unnamed contractors. You know who's actually doing the work.
Book the Technology Strategy Assessment →